
SSO Guide (Deprecated)
Deprecated. See OAuth2 guides
How to configure SSO
SSO require additionaly to configure TLS for application, in that example we will use self-signed certificate, in case of use legal certificates please skip step 1.
Step 1
At this step we will generate self-signed PKCS12 keypair.
mkdir cert
keytool -genkeypair -alias ui-for-apache-kafka -keyalg RSA -keysize 2048 \
  -storetype PKCS12 -keystore cert/ui-for-apache-kafka.p12 -validity 3650
Step 2
Create new application in any SSO provider, we will continue with Auth0.
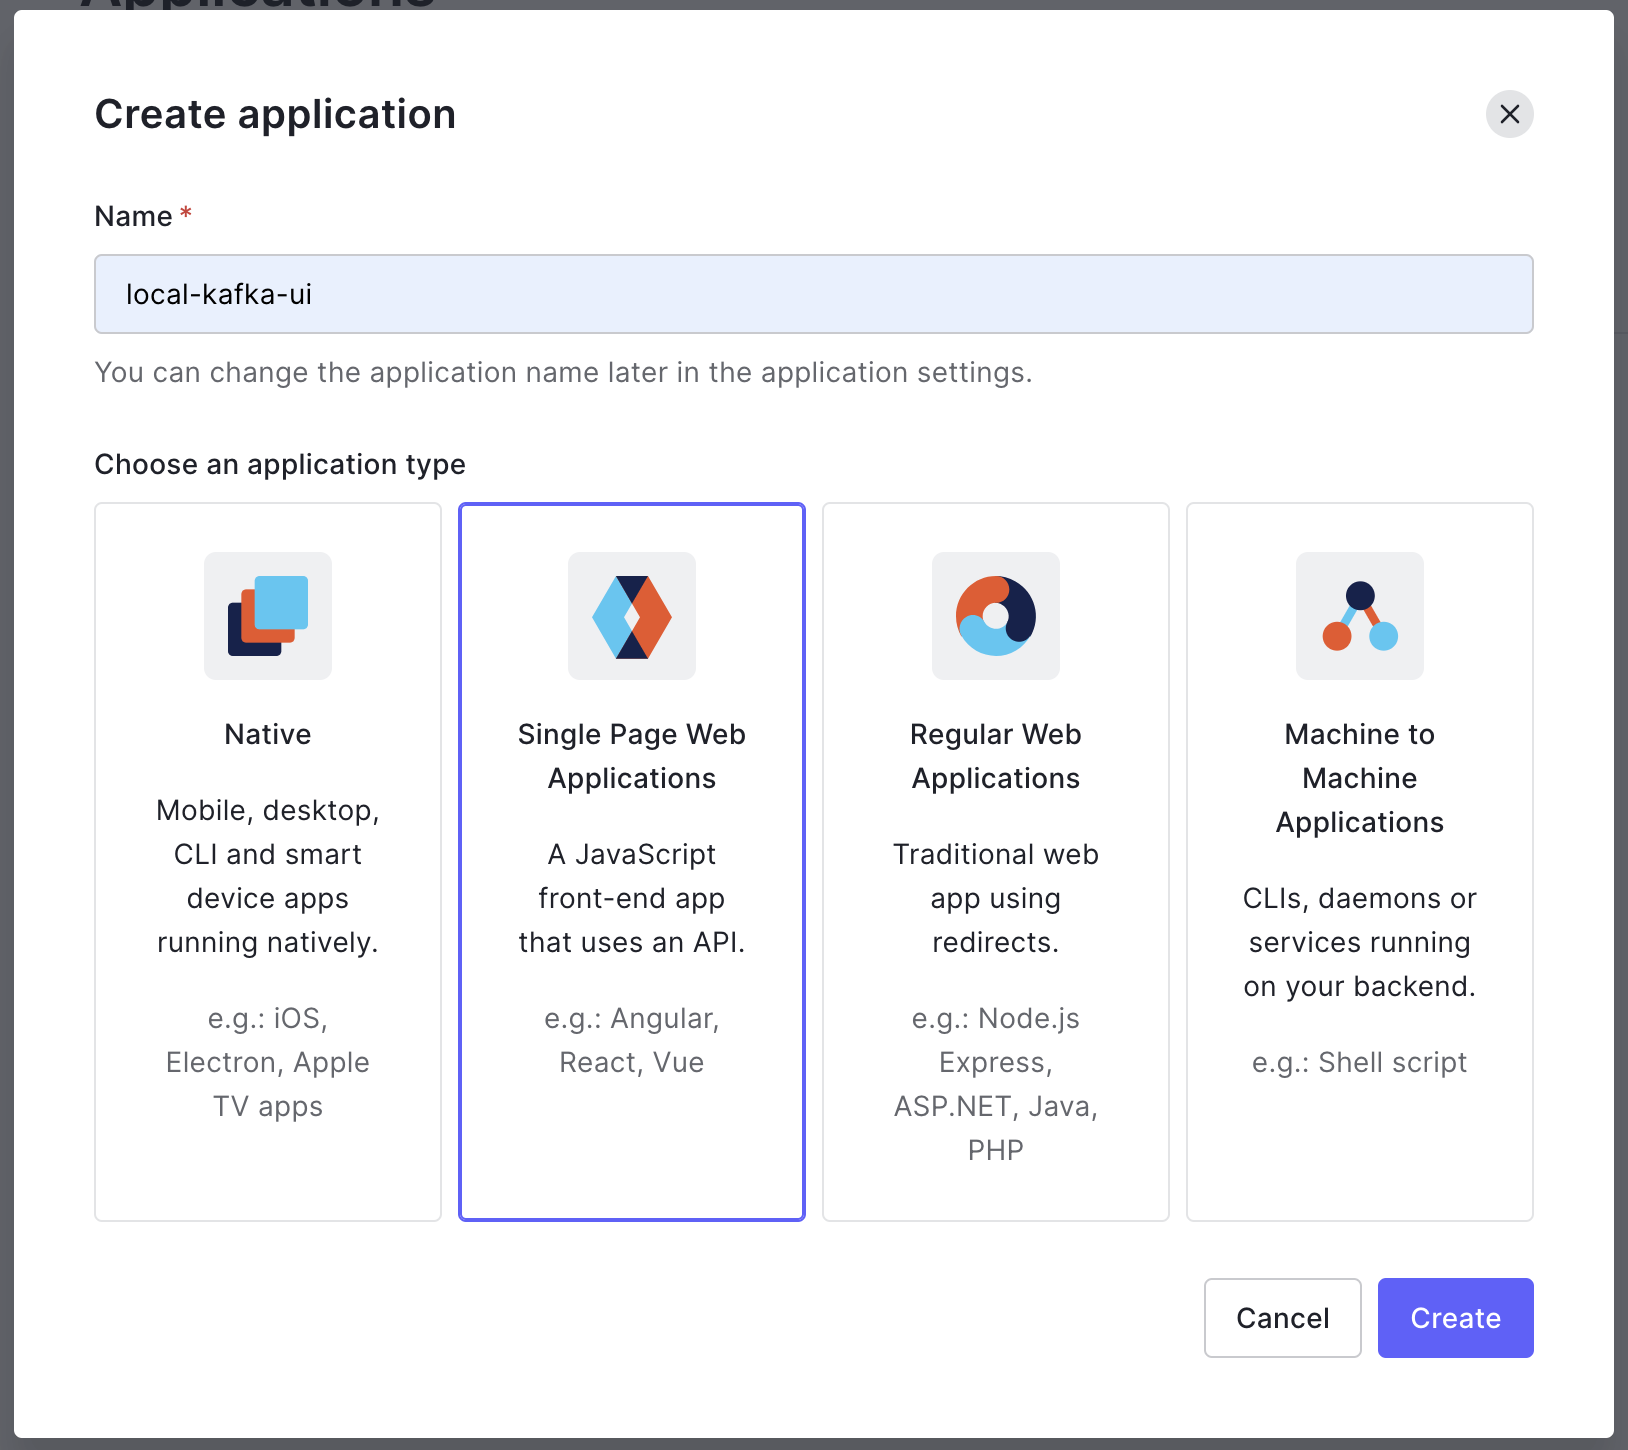
After that need to provide callback URLs, in our case we will use https://127.0.0.1:8080/login/oauth2/code/auth0
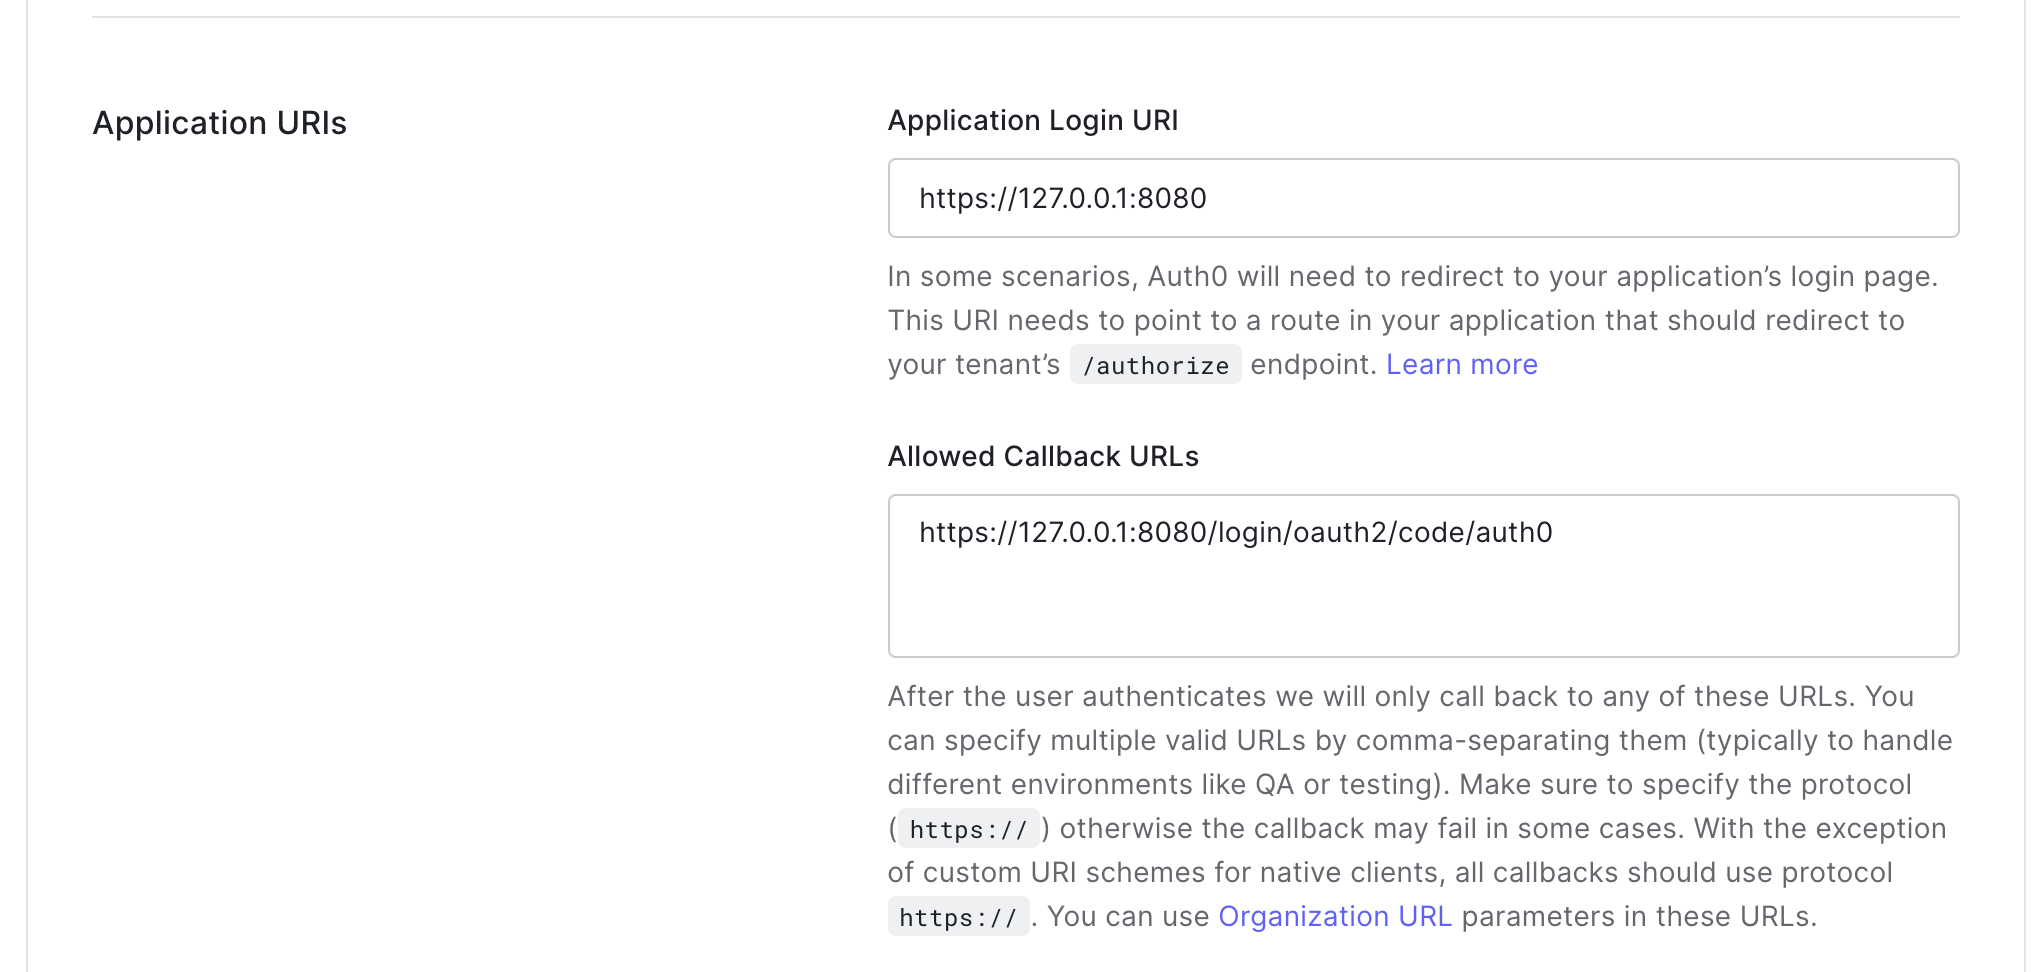
This is a main parameters required for enabling SSO
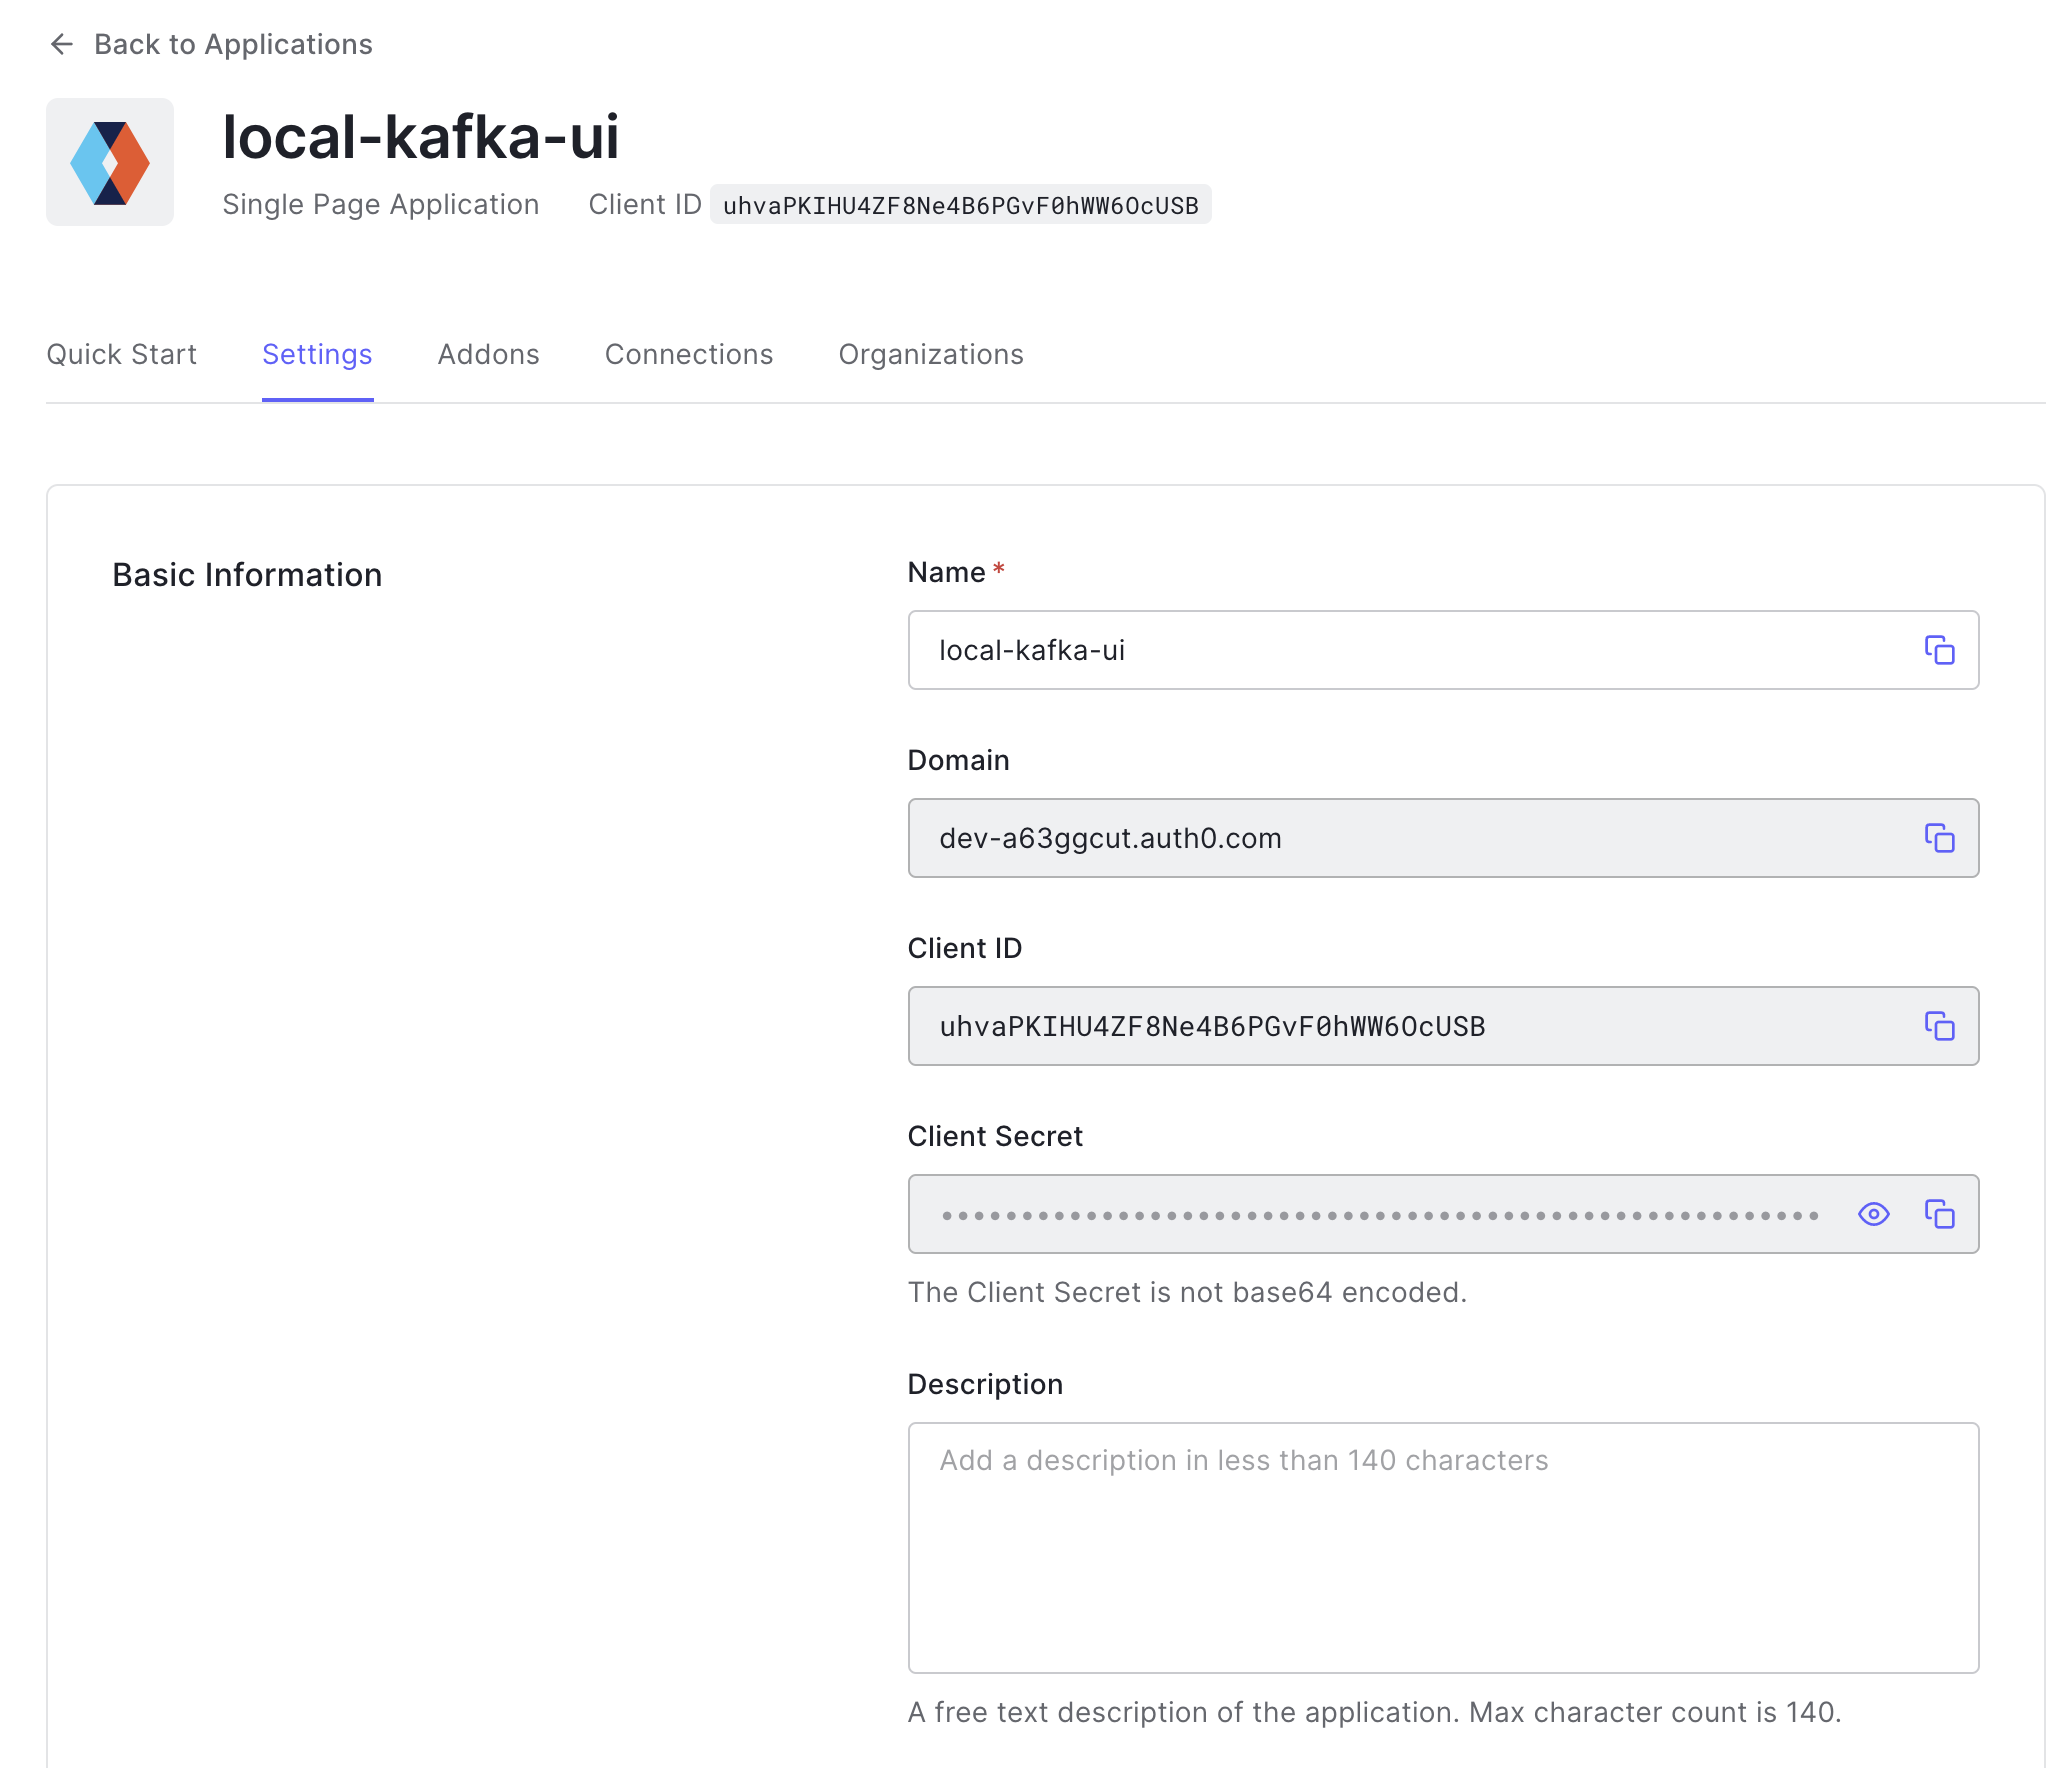
Step 3
To launch Kafbat UI with enabled TLS and SSO run following:
In the case with trusted CA-signed SSL certificate and SSL termination somewhere outside of application we can pass only SSO related environment variables:
Step 4 (Load Balancer HTTP) (optional)
If you're using load balancer/proxy and use HTTP between the proxy and the app, you might want to set server_forward-headers-strategy to native as well (SERVER_FORWARDHEADERSSTRATEGY=native), for more info refer to this issue.
Step 5 (Azure) (optional)
For Azure AD (Office365) OAUTH2 you'll want to add additional environment variables:
Note that scope is created by default when Application registration is done in Azure portal. You'll need to update application registration manifest to include "accessTokenAcceptedVersion": 2
Last updated
Was this helpful?